New CKS Test Forum, CKS Brain Exam
BONUS!!! Download part of Exams4Collection CKS dumps for free: https://drive.google.com/open?id=1uOm5AjwCKMPEKDgmjpuQ3XhnUjHhCqcb
Now our CKS practice materials have won customers' strong support. Our sales volume is increasing every year. The great achievements benefit from our enormous input. First of all, we have done good job on researching the new version of the CKS exam question. So you will enjoy the best learning experience every once in a while. Also, the quality of our CKS Real Dump is going through the official inspection every year. So you can fully trust us. If you still have suspicion of our CKS practice materials, you can test by yourself. Welcome to select and purchase.
Linux Foundation CKS Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Cluster Hardening | 15% | - Authentication and authorization - API server security |
| Supply Chain Security | 20% | - Secure CI/CD practices - Image scanning and verification |
| Cluster Setup | 15% | - Secure installation configuration - Hardening cluster components |
| System Hardening | 15% | - Host security controls - Kernel and node security configuration |
| Monitoring, Logging and Runtime Security | 15% | - Runtime threat detection - Audit logging and monitoring |
| Minimizing Microservice Vulnerabilities | 20% | - Container isolation and security contexts - Pod security standards |
CKS Brain Exam | Valid CKS Test Cost
Our company deeply knows that product quality is very important, so we have been focusing on ensuring the development of a high quality of our CKS test torrent. All customers who have purchased our products have left deep impression on our CKS guide torrent. Of course, the customer not only has left deep impression on the high quality of our products but also the efficiency of our products. Our CKS Exam Questions can help you save much time, if you use our CKS study prep, you just need to spend 20-30 hours on learning, and you will pass your CKS exam successfully.
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions (Q58-Q63):
NEW QUESTION # 58
You have a Kubernetes cluster that runs a critical application This application uses sensitive data stored in a persistent volume that is accessible only by the pods running the application. You want to ensure that if any pod is compromised, the attacker cannot gain access to this sensitive data What security best practices would you implement?
Answer:
Explanation:
Solution (Step by Step) :
1. Volume Encryption:
- Encrypt the persistent volume at rest using tools like BitLocker or LUKS-
- Ensure that encryption keys are stored securely, ideally outside the Kubernetes cluster-
- use a key management system to manage encryption keys securely.
- Use a separate encryption key for each volume.
2. Access Control:
- Restrict access to the persistent volume to only the pods running the critical application.
- Utilize Kubernetes RBAC to grant minimal permissions to the service accounts responsible for running the application pods.
- Avoid granting broad permissions to service accounts, limiting their access to only the necessary resources.
3. Pod security Policies (PSP):
- Implement PSPs to limit the capabilities and resources available to pods.
- Restrict pods from accessing sensitive volumes or having privileged permissions.
- Enforce policies that prevent pods from mounting volumes that are not explicitly authorized.
- Define strict PSP rules to limit the potential impact of compromised pods.
4. Network Segmentation:
- Isolate the Kubernetes cluster from other networks and restrict inbound and outbound traffic to only authorized sources and destinations.
- Implement firewall rules to prevent unauthorized access to the cluster.
- Utilize network segmentation to prevent attackers from gaining access to the persistent volume via network connections.
5. Runtime Security:
- Use runtime security tools like Falco or Kubernetes Admission Controllers to monitor and prevent malicious activity within pods.
- Configure runtime security tools to detect and block attempts to access sensitive data within the persistent volume.
- Implement intrusion detection and prevention systems (IDS/IPS) within the Kubernetes environment
6. Regular Security Audits:
- Conduct regular security audits to ensure that security controls are effective.
- Evaluate the effectiveness of encryption, access control, and runtime security measures.
- Identify and remediate any security vulnerabilities promptly.
7. Immutable Infrastructure:
- Use immutable infrastructure principles to minimize the attack surface and prevent attackers from modifying persistent volumes.
- Deploy application code and configurations as immutable containers-
- Avoid making changes to persistent volumes directly.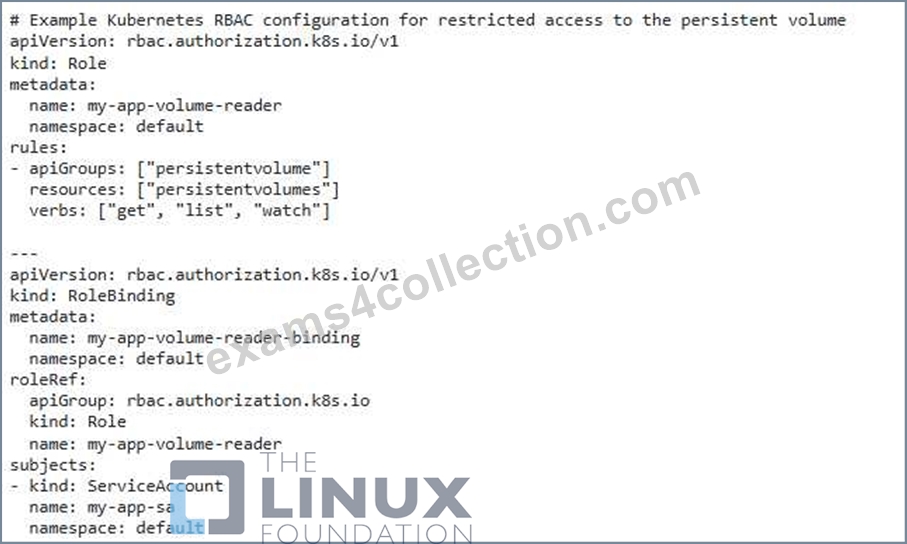
NEW QUESTION # 59
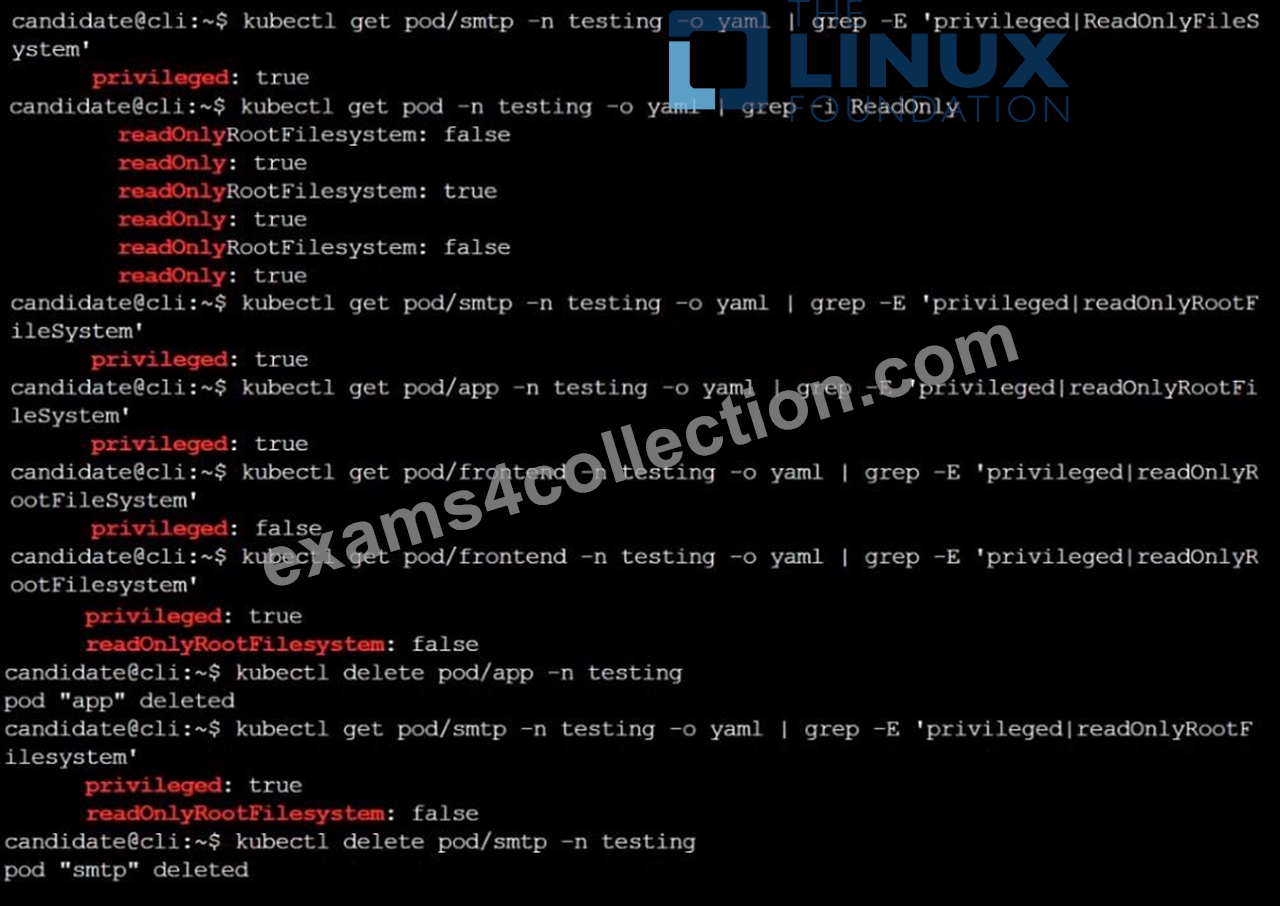
You must complete this task on the following cluster/nodes: Cluster: immutable-cluster Master node: master1 Worker node: worker1 You can switch the cluster/configuration context using the following command: [desk@cli] $ kubectl config use-context immutable-cluster Context: It is best practice to design containers to be stateless and immutable. Task: Inspect Pods running in namespace prod and delete any Pod that is either not stateless or not immutable. Use the following strict interpretation of stateless and immutable: 1. Pods being able to store data inside containers must be treated as not stateless. Note: You don't have to worry whether data is actually stored inside containers or not already. 2. Pods being configured to be privileged in any way must be treated as potentially not stateless or not immutable.
Answer:
Explanation: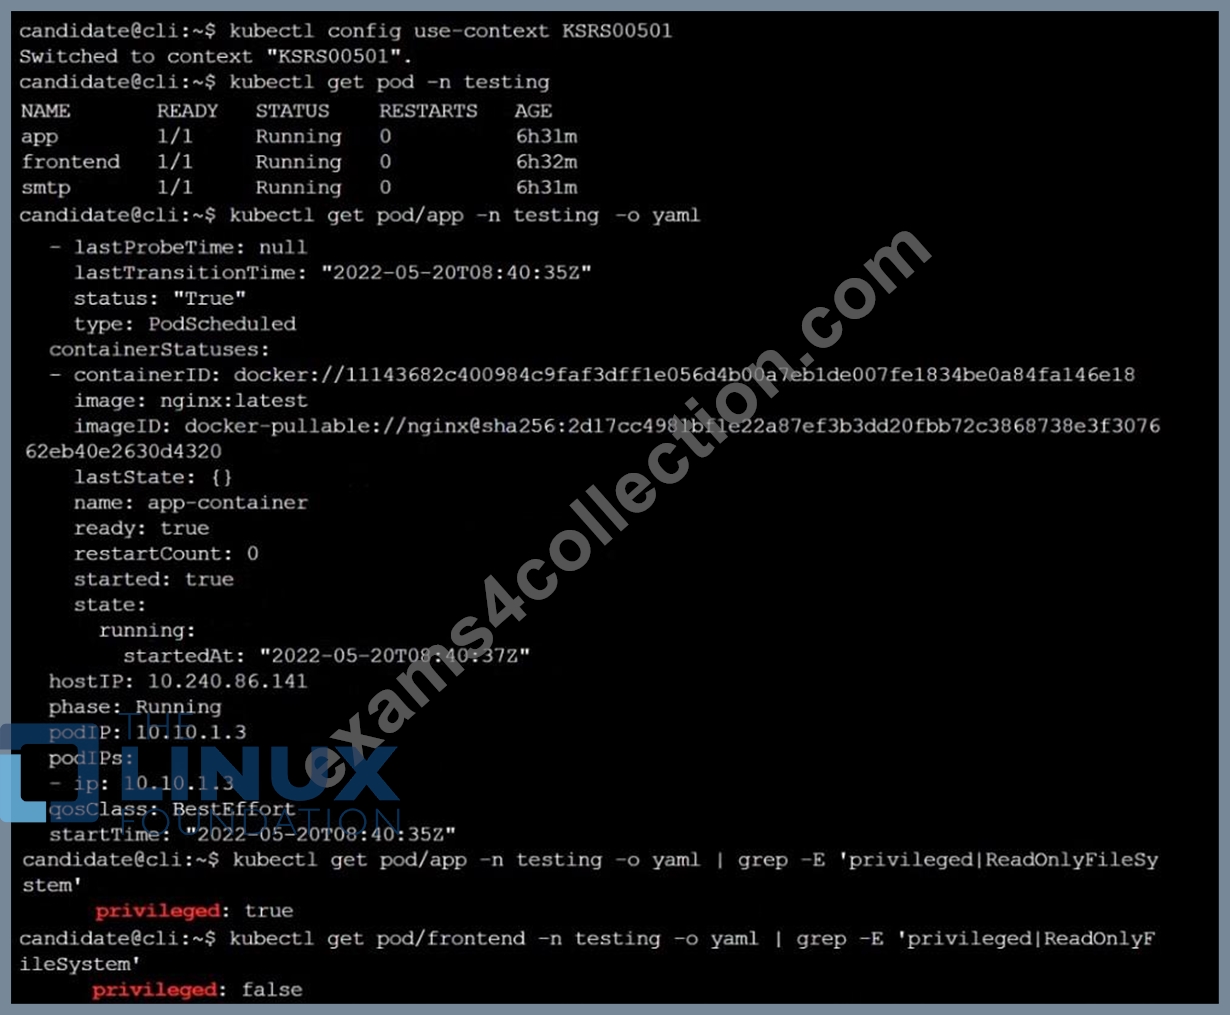
Reference: https://kubernetes.io/docs/concepts/policy/pod-security-policy/ https://cloud.google.com/architecture/best-practices-for-operating-containers
NEW QUESTION # 60
Analyze and edit the given Dockerfile
FROM ubuntu:latest
RUN apt-get update -y
RUN apt-install nginx -y
COPY entrypoint.sh /
ENTRYPOINT ["/entrypoint.sh"]
USER ROOT
Fixing two instructions present in the file being prominent security best practice issues Analyze and edit the deployment manifest file apiVersion: v1 kind: Pod metadata:
name: security-context-demo-2
spec:
securityContext:
runAsUser: 1000
containers:
- name: sec-ctx-demo-2
image: gcr.io/google-samples/node-hello:1.0
securityContext:
runAsUser: 0
privileged: True
allowPrivilegeEscalation: false
Fixing two fields present in the file being prominent security best practice issues Don't add or remove configuration settings; only modify the existing configuration settings Whenever you need an unprivileged user for any of the tasks, use user test-user with the user id 5487
Answer:
Explanation:
FROM debian:latest
MAINTAINER k@bogotobogo.com
# 1 - RUN
RUN apt-get update && DEBIAN_FRONTEND=noninteractive apt-get install -yq apt-utils RUN DEBIAN_FRONTEND=noninteractive apt-get install -yq htop RUN apt-get clean
# 2 - CMD
#CMD ["htop"]
#CMD ["ls", "-l"]
# 3 - WORKDIR and ENV
WORKDIR /root
ENV DZ version1
$ docker image build -t bogodevops/demo .
Sending build context to Docker daemon 3.072kB
Step 1/7 : FROM debian:latest
---> be2868bebaba
Step 2/7 : MAINTAINER k@bogotobogo.com
---> Using cache
---> e2eef476b3fd
Step 3/7 : RUN apt-get update && DEBIAN_FRONTEND=noninteractive apt-get install -yq apt-utils
---> Using cache
---> 32fd044c1356
Step 4/7 : RUN DEBIAN_FRONTEND=noninteractive apt-get install -yq htop
---> Using cache
---> 0a5b514a209e
Step 5/7 : RUN apt-get clean
---> Using cache
---> 5d1578a47c17
Step 6/7 : WORKDIR /root
---> Using cache
---> 6b1c70e87675
Step 7/7 : ENV DZ version1
---> Using cache
---> cd195168c5c7
Successfully built cd195168c5c7
Successfully tagged bogodevops/demo:latest
NEW QUESTION # 61
SIMULATION
Context
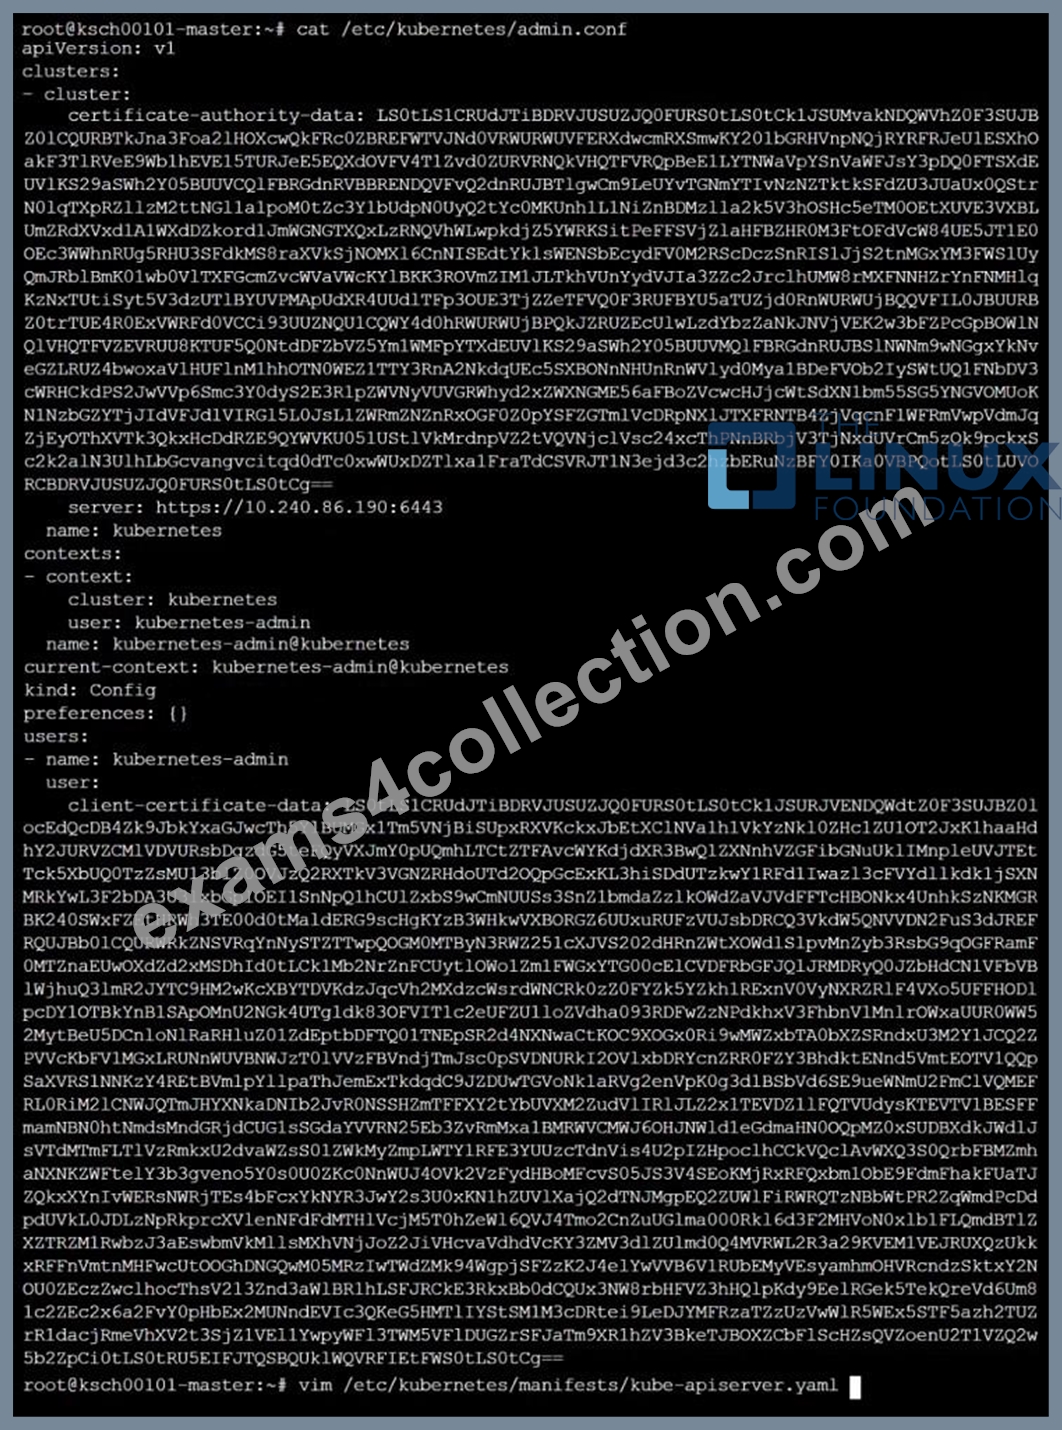
The kubeadm-created cluster's Kubernetes API server was, for testing purposes, temporarily configured to allow unauthenticated and unauthorized access granting the anonymous user duster-admin access.
Task
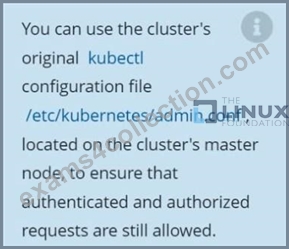
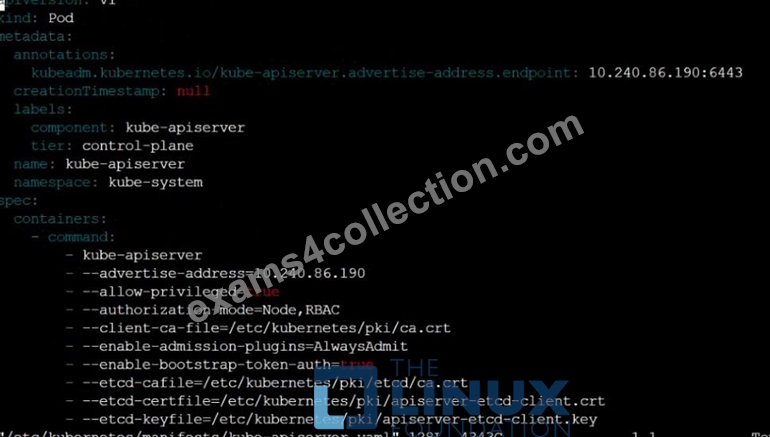
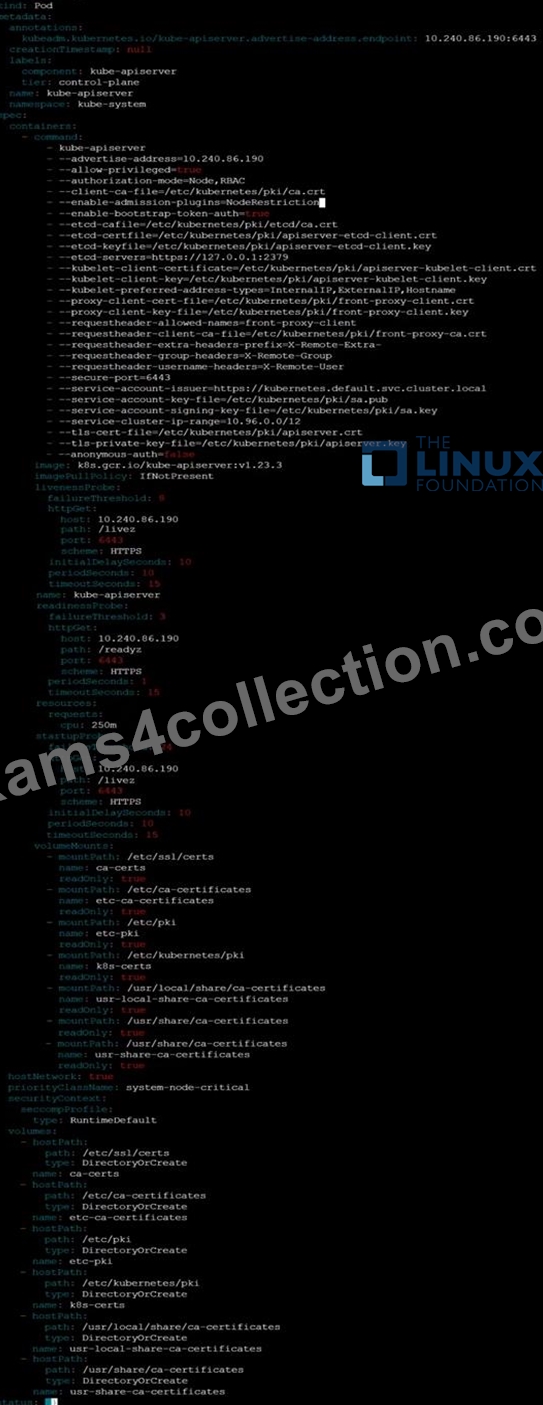
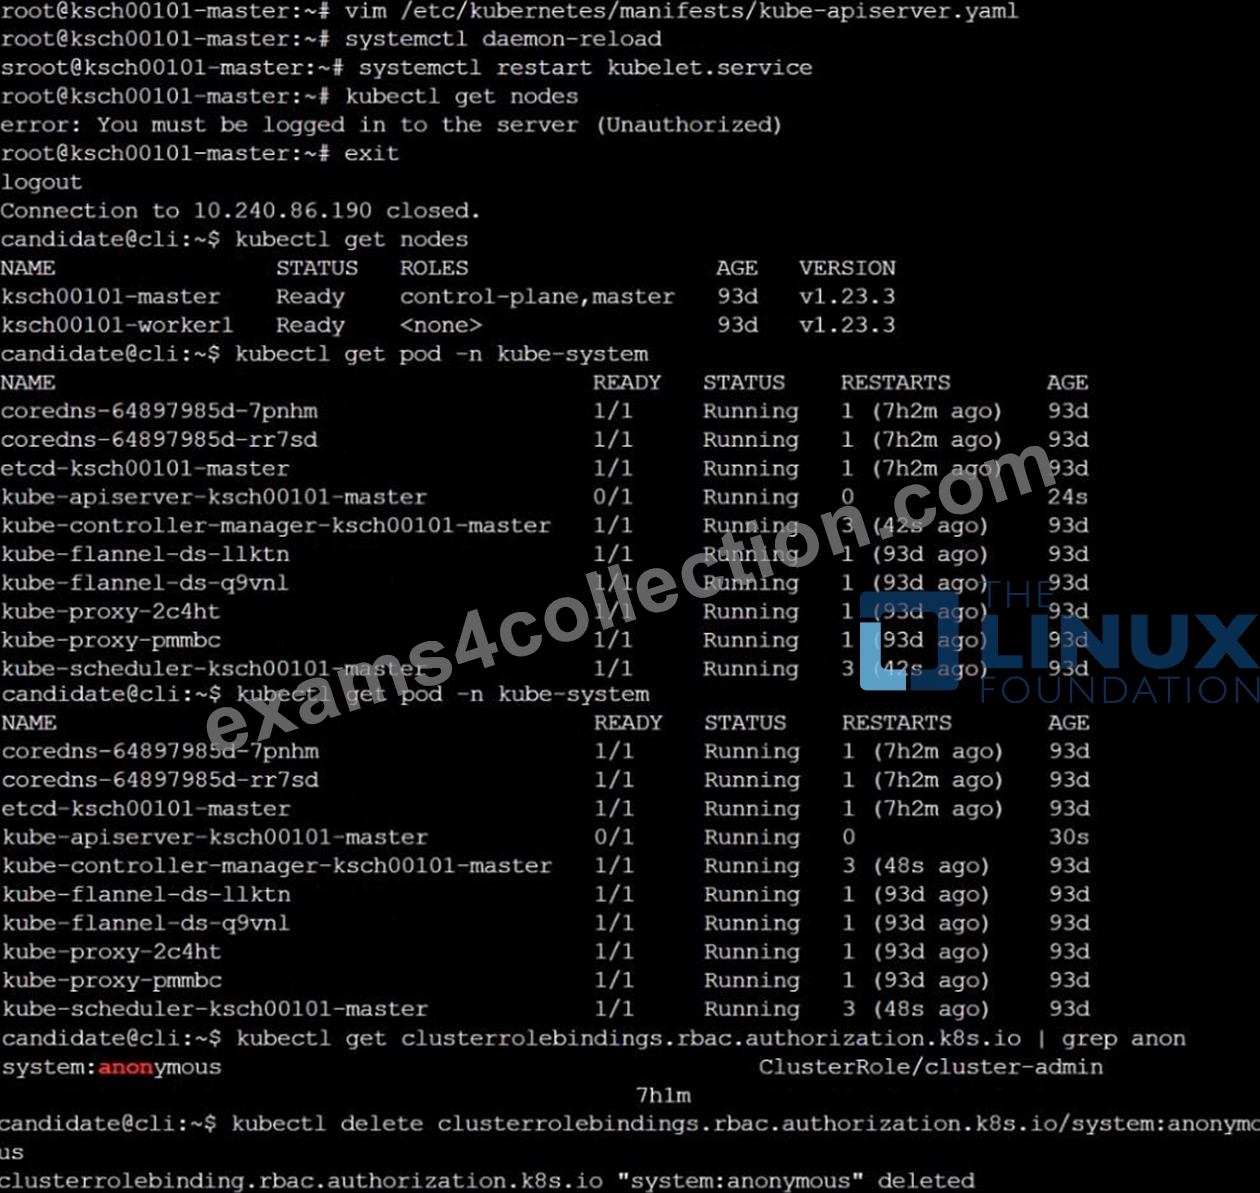
Reconfigure the cluster's Kubernetes API server to ensure that only authenticated and authorized REST requests are allowed.
Use authorization mode Node,RBAC and admission controller NodeRestriction.
Cleaning up, remove the ClusterRoleBinding for user system:anonymous.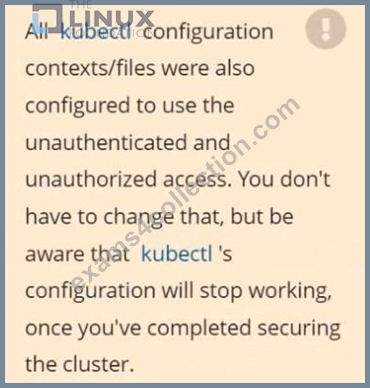
Answer:
Explanation:
See the Explanation below
Explanation: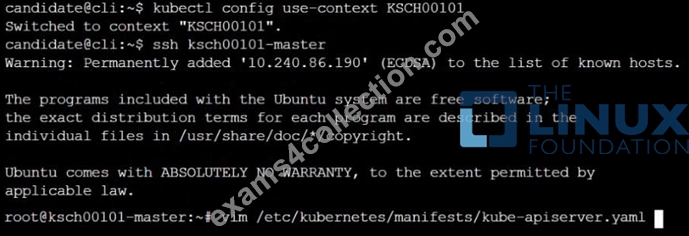
NEW QUESTION # 62
You are running a critical application in a Kubernetes cluster. You need to implement a solution to detect and respond to potential security threats within your application containers. Specifically, you want to monitor for unauthorized file system modifications, suspicious network connections, and unusual process behavior. How would you design and implement a container security solution using tools like Falco, AppArmor, and Kubernetes Admission Controllers to achieve these objectives?
Answer:
Explanation:
Solution (Step by Step):
1. Install and Configure Falco:
- Install Falco using the official Helm charts:
bash
helm repo add falco httpsflfalco.org/charts
helm install falco falco/falco
- Customize the Falco rules to detect specific threats: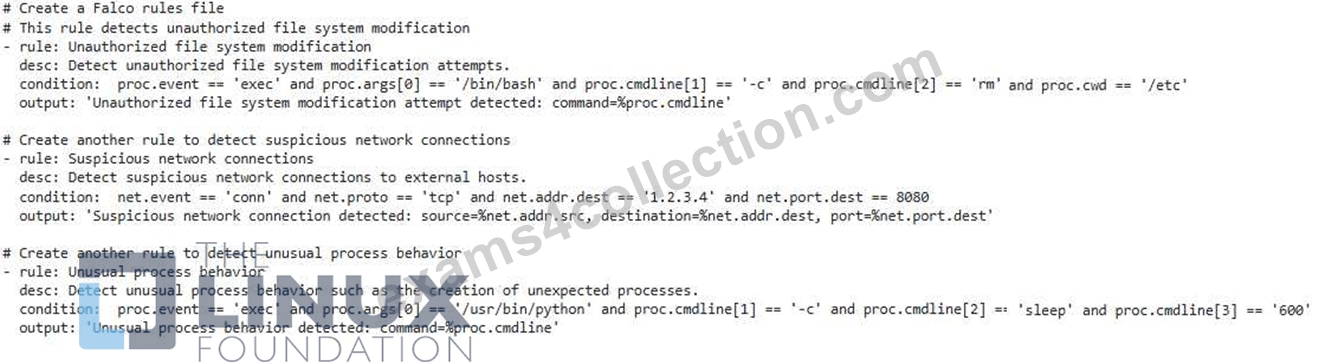
2. Configure AppArmor: - Create a custom AppArmor profile for your application container: # Create a new AppArmor profile sudo nano /etc/apparmor.d/your-app-profile - Configure the profile to restrict file system access, network connections, and process execution: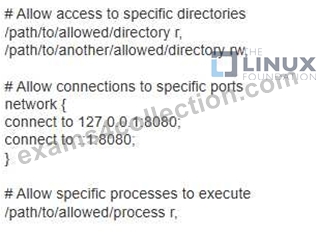
- Load and enable the AppArmor profile: bash sudo apparmor_parser -r letc./apparmor.d/your-app-profile sudo systemctl restart apparmor 3. Implement Kubernetes Admission Controllers: - Use Kubernetes Admission Controllers to enforce container security policies at pod creation time: - Define a custom Admission Webhook to check for vulnerabilities: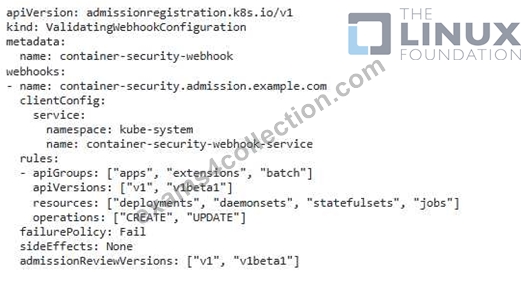
- Create a Deployment to run the Admission Controller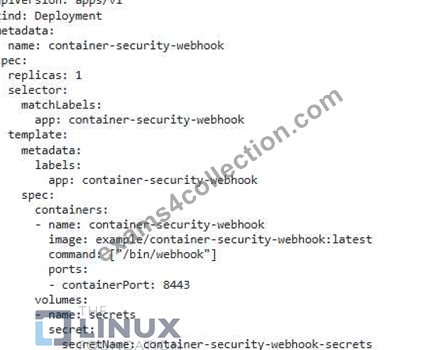
4. Integrate and Monitor: - Integrate the Falco rules, AppArmor profile, and Kubernetes Admission Controllers within your Kubernetes Cluster - Monitor Falco alerts, AppArmor logs, and Kubernetes events to identify and investigate potential threats. This solution provides a comprehensive approach to container security, allowing you to detect and respond to threats proactively.
NEW QUESTION # 63
......
You can become part of this skilled and qualified community. To do this joust enroll in the Exams4Collection Linux Foundation CKS certification exam and start preparation with real and valid Certified Kubernetes Security Specialist (CKS) (CKS) exam practice test questions right now. The Exams4Collection CKS Exam Practice test questions are checked and verified by experienced and qualified CKS exam trainers. So you can trust Exams4Collection Linux Foundation CKS exam practice test questions and start preparation with confidence.
CKS Brain Exam: https://www.exams4collection.com/CKS-latest-braindumps.html
- DOWNLOAD the newest Exams4Collection CKS PDF dumps from Cloud Storage for free: https://drive.google.com/open?id=1uOm5AjwCKMPEKDgmjpuQ3XhnUjHhCqcb